VMSA-2026-0008: Brotli RCE on SDDC Manager, Workaround Only for Now
No patch for CVE-2026-111497 yet. On SDDC Manager 9.1.1.x the score is 9.8 and 443 alone is not enough — cover port 7500 too, and re-check after every upgrade.
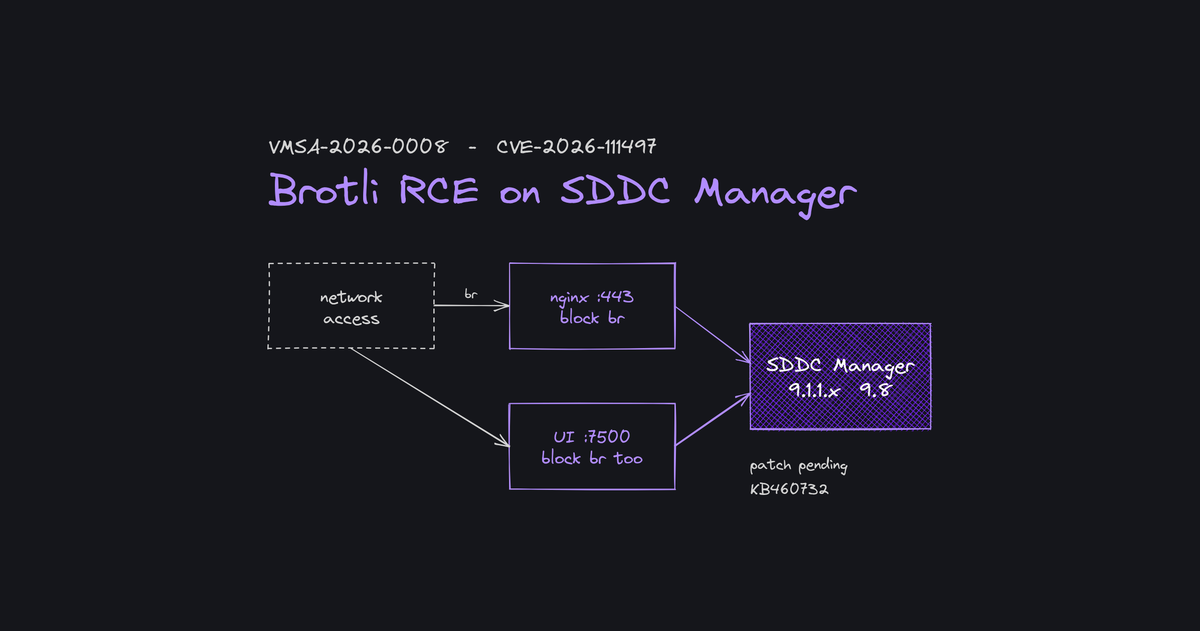
No patch yet. On SDDC Manager 9.1.1.x the score is 9.8, the attacker needs only network access, and the Fixed Version column still says Patch pending. Apply the workaround now.
VMSA-2026-0008 (27 October 2026, revision .1 the next day) covers one CVE: CVE-2026-111497, an out-of-bounds write in the Node.js Brotli decoder used by SDDC Manager. A malicious actor with network reach to the appliance can execute arbitrary code. Broadcom rated the advisory Critical, CVSSv3 7.5 to 9.8 — and the critical end of that range is 9.1.1.x only.
Version, score, KB
| SDDC Manager | CVSSv3 | Severity | Fixed version | Workaround |
|---|---|---|---|---|
| 9.1.1.x | 9.8 | Critical | Patch pending | KB460732 |
| 9.0.x, 9.1.0 | 7.5 | Important | Patch pending | KB460734 |
| 5.2.x | 7.5 | Important | Patch pending | KB460734 |
5.1.x and earlier are not affected.
The score gap is in the vectors: 9.1.1.x is network, low complexity, no privileges (AV:N/AC:L/PR:N/UI:N). Older releases are adjacent network and high complexity (AV:A/AC:H). Still affected, still unpatched — just harder to hit.
Broadcom reviewed the rest of the portfolio for this CVE. Nothing else is critically affected except SDDC Manager in VCF 9.1.1 (KB460791).
Why 443 alone is not enough (9.1.1.x)
The 9.1.1 workaround rejects request bodies with Content-Encoding: br before any parser sees them. Two paths:
- nginx on 443 — Brotli bodies get HTTP 415.
- UI server on port 7500 — middleware in the UI app does the same. nginx never sees traffic aimed straight at the UI on localhost port 7500.
Covering only nginx on 443 leaves the UI on port 7500 open. Both paths have to be locked; the KB covers both. The script does both; a manual change must do both too.
Before touching anything: snapshot or backup the appliance, and wait until no SDDC Manager task is running (upgrade, workload domain, certificate replacement). SSH as vcf, then root. Download the remediation script from the KB. If it came through Windows, strip CRLF first:
sed -i 's/\r$//' CVE-2026-111497_VCF911x_remediation.sh
Then as root:
bash CVE-2026-111497_VCF911x_remediation.sh check
bash CVE-2026-111497_VCF911x_remediation.sh apply
check changes nothing. apply backs up what it edits, puts the workaround in place, restarts the UI and verifies. Rollback only if something breaks:
bash CVE-2026-111497_VCF911x_remediation.sh rollback
Manual nginx / app.js edits and the verification curls stay in the KB. Prefer the script or the manual path — not both — and roll back with the same method used to apply.
Older releases: a different fix
On 5.2.x, 9.0.x and 9.1.0 the workaround does not touch nginx. It preloads nobrotli.cjs, which removes zlib.createBrotliDecompress from the UI Node.js process (the decoder axios uses), via NODE_OPTIONS on the sddc-manager-ui-app unit. Same check / apply / rollback pattern, different script:
bash CVE-2026-111497_pre911_remediation.sh check
bash CVE-2026-111497_pre911_remediation.sh apply
Do not cross the KBs: the 9.1.1 procedure is for 9.1.1 only; the preload procedure is for the older line only.
Upgrades can undo the work
An upgrade to a build that still ships the unfixed Node.js runtime silently drops the workaround. After every SDDC Manager upgrade, run check again until a fixed release is installed. Both workarounds are temporary, and only meant for this CVE.
Bottom line
Inventory every SDDC Manager and its exact version. On 9.1.1.x, apply the dual-path workaround now and confirm 443 and port 7500 are both covered. On 9.0.x, 9.1.0 and 5.2.x, apply the preload workaround. Restrict management-plane access to the hosts that actually need it — the advisory's only stated condition for exploitation is network access. Watch the Fixed Version column on VMSA-2026-0008 for when patches land.
Sources
- Broadcom VMSA-2026-0008.1: Node.js Brotli decoder out-of-bounds write remote code execution vulnerability (CVE-2026-111497), updated 28 Oct 2026
- Broadcom KB 460732: Manual interim workaround for CVE-2026-111497 (Brotli) on SDDC Manager 9.1.1.x
- Broadcom KB 460734: Manual interim workaround for CVE-2026-111497 (Brotli) on SDDC Manager 5.2.x, 9.0.2, 9.1.0
- Broadcom KB 460791: Node.js Brotli decoder vulnerability, CVE-2026-111497, and VMware by Broadcom product portfolio