Explore on Tour Frankfurt recap: one product, a patch flood, and no vSphere Standard
Two days at Kap Europa, one real announcement (HyperArmor), a confirmed monthly patch cadence, and silence on vSphere Standard. My recap and what I would do next.
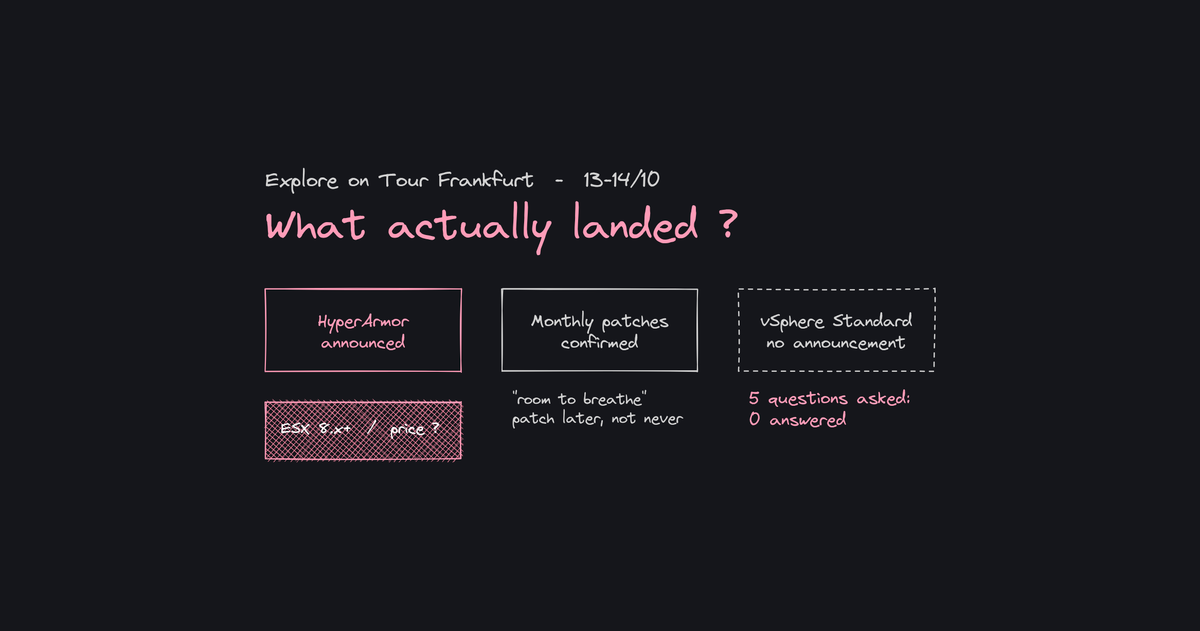
Explore on Tour Frankfurt ran on 13-14 October at Kap Europa. It produced one product announcement, a confirmed monthly patch cadence, and no news on vSphere Standard.
HyperArmor, the only announcement
HyperArmor was announced on day 1; day 2 added nothing. It is a paid security add-on at the ESX layer with three functions:
- Host-level virtual patching: blocks exploit attempts on the host, with no reboot and no software upgrade.
- Positive security: an allowlist of known-good processes and scripts; anything else is blocked by default, and new scripts need admin approval.
- MFA for ESX SSH: SSH credentials plus a TOTP challenge tied to a separate identity.
It supports ESX 8.x and later and needs no agent in guest VMs. Pricing has not been published.
Paul Turner (CPO, VCF Division), in the press release: "When attacks come at machine speed, reactive detection and patching are no longer enough."
- Scope. The press release covers "the VMware ESX hypervisor component of VMware Cloud Foundation". The VCF blog calls it "purpose-built for VCF and VMware vSphere Foundation", and the solution brief says to deploy it "across VCF and VVF stacks". Standalone vSphere is not mentioned.
- Origin. According to The Register, it was built by Broadcom's Symantec and Carbon Black teams.
- Availability. TechTarget reports it is "expected to ship in the first quarter of Broadcom's fiscal 2027, which starts in November". Broadcom has not published a date.
The patch cadence
Prashanth Shenoy (VP product marketing, VCF division) told The Register that VMware has moved to monthly software updates, partly because AI now finds many more flaws, and that customers need "room to breathe". HyperArmor is positioned as that buffer, not a replacement for patching. Eric Chen on day 1: "We always still want you to patch; that is the right thing to do, but this basically buys you time."
The last critical advisory is VMSA-2026-0006, published on 29 July and updated on 19 August, covering ESX, vCenter, Workstation and Fusion.
With monthly updates, a quarterly maintenance window no longer fits. What I plan with customers:
- Start using live patching on a non-critical cluster. The vSphere 9.1 comparison datasheet lists "Live Patching for ESX" in every edition, Standard included.
- Define what "tested" means (backup jobs, storage plugins, monitoring agents) so a monthly patch is routine.
- If you buy HyperArmor, track every shielded CVE with a deadline. As Futurum puts it: "Every deferred patch is remediation debt."
Paying for MFA
According to The Register, SSH MFA on ESX comes through HyperArmor, so customers pay extra for it. Futurum calls security as a monetization lever "defensible", but says charging separately for controls like SSH MFA, after licensing changes that led cloud providers to file a competition complaint in the EU, "will test goodwill". Stephanie Walter (HyperFrame Research) in TechTarget: "Where does foundational security end and premium protection begin?" Shenoy's answer: "Not every environment needs that layer. Customers with higher-risk workloads add it, and customers with lower exposure don't have to."
The free first step: check who needs SSH on your hosts. If it is enabled everywhere "just in case", close it.
vSphere Standard: no-show
The five questions raised before the event:
- Which version? No answer.
- Which features? No answer.
- Any core limit? No answer.
- Downgrade path? No answer.
- What about customers already pushed to VVF/VCF? No answer.
On 2 September, The Register reported Paul Turner saying more details would likely emerge as Explore came to Germany. They did not. Heise reported memory tiering as a possible feature and a target of environments around 128 cores. On 11 October, reseller Eurokommerz wrote that, as of 10 October, it had no Broadcom document with a version or date. The vSphere 9.1 comparison datasheet still says Standard and Enterprise Plus "are only available as versions up to the 8 Update 3 release". The HyperArmor press release mentions no vSphere edition.
Don't sign a multi-year renewal on a promise. Keep these five questions until Broadcom publishes something.
Takeaway
Frankfurt was a security-and-cadence event, not a licensing one. HyperArmor answers a real problem, but as a paid add-on to an already expensive stack — and SSH MFA should be native, not a line item. The five questions small customers brought to Kap Europa went unanswered, and that silence was the loudest thing in the room. We'll be watching Tokyo and London for whether Broadcom finally says something. I'll keep everyone posted with an update.
Sources
- Broadcom - Broadcom Introduces VMware HyperArmor (press release, 13/10/2026) - also on GlobeNewswire via Nasdaq
- VCF blog - Proactive Defense: Enhancing Hypervisor Security in the AI Era (13/10/2026)
- VMware - HyperArmor solution brief
- The Register - VMware is pushing so many patches... (13/10/2026)
- TechTarget - Broadcom armors VMware ESX hypervisor with virtual patching (13/10/2026)
- SiliconANGLE - Broadcom adds hypervisor protection to VMware (13/10/2026)
- SDxCentral - Broadcom arms VMware security with HyperArmor (13/10/2026)
- Futurum - HyperArmor brings virtual patching to the hypervisor (14/10/2026)
- SecurityOnline - Broadcom announces VMware monthly security updates (14/10/2026)
- SecNews - VMware HyperArmor adds virtual patching and MFA to ESX hosts (13/10/2026)
- Broadcom - VMSA-2026-0006
- VMware - vSphere 9.1 product line comparison
- The Register - vSphere Standard upgrade promised (02/09/2026)
- heise online - Broadcom plans new vSphere Standard (03/09/2026)
- Eurokommerz - vSphere Standard and VVF end of life (11/10/2026)
- Broadcom marketing on LinkedIn - Frankfurt registration open (03/07/2026)
- VMware Explore (tour dates)